By Naveen Kumar Sharma
Security teams working in cloud-native environments face a familiar dilemma: how to ship code quickly, meet compliance requirements, and reduce vulnerabilities without slowing developers down or breaking their momentum. Legacy tools often create more noise than clarity, surfacing issues too late, when fixes are slow, expensive, and frustrating for everyone involved.
From my experience helping teams secure their delivery pipelines, the most significant wins always come from embedding security early, right in the build process, before risk has a chance to spread. One of the most effective and scalable approaches I’ve used is generating Software Bills of Materials (SBOMs) within CI/CD and scanning them using Amazon Inspector.
This approach enables teams to gain visibility, mitigate risk, and establish trust with both engineering teams and auditors. Here’s how this works in practice and how your team can adopt the same pattern.
The Value of Early Risk Visibility
You can’t fix what you can’t see. From package dependencies to base images and internal libraries, hidden risks can slip past traditional testing gates, but they’re rarely visible in traditional test or deploy stages. Too often, teams don’t discover what’s inside their containers or functions until a late-stage scan flags something urgent, by which point remediating it is slower and more expensive.
SBOMs flip that equation. They provide a complete inventory of every component, whether it’s a container image or a Lambda function. When generated as part of the development pipeline, SBOMs offer a continuously updated inventory of everything your software depends on.
Early visibility accelerates resolution, enhances auditability, and earns stakeholder trust.
Deploying SBOMs with Amazon Inspector
Since late 2023, Amazon’s SBOM Generator CLI has become my go-to for integrating secure artifact visibility into CI/CD pipelines. It’s fast, lightweight, and supports CycloneDX, one of the most widely adopted formats for software supply chain tooling. Whether running locally or inside a CI runner, it’s built for seamless integration.
Getting started is simple. Here’s how to install and verify it:
Figure 1: Installation process for the Amazon SBOM Generator CLI. Created by Naveen Sharma.

Once installed, generating a basic SBOM for a container image is simple:
Figure 2: Command to generate a basic SBOM for a container image using inspector-sbomgen. Created by Naveen Sharma.

For more advanced workflows, like sending the SBOM to Inspector for vulnerability analysis, the CLI accepts additional flags:
Figure 3: Advanced usage of inspector-sbomgen with scan flags and AWS region for Inspector integration. Created by Naveen Sharma.

The tool is compatible with most Linux-based CI runners and supports Docker environments by default. Output can be stored locally, uploaded to S3, or streamed to other systems for further analysis.
Building Secure CI/CD Workflows
In fast-moving pipelines, even minor delays can tempt teams to skip security checks. That’s why SBOMs and Inspector scans need to fit naturally into CI/CD jobs, rather than feel like separate workflows.
In my experience, most teams add SBOM generation right after a successful build. Results can be saved to an artifact store, logged centrally, or scanned immediately using Inspector. Teams using Jenkins, GitHub Actions, or GitLab CI/CD can trigger these jobs conditionally or on every commit.
Event-driven scans, triggered when a new container is published or source tags are updated, provide security without slowing down delivery.
Insights That Developers Can Act On
Amazon Inspector plays a key role in making SBOMs useful. It scans the dependency list, maps packages to CVEs, and provides contextual findings. Instead of flooding engineers with vague alerts that lead nowhere, Inspector highlights precise, actionable issues, like a specific version of a vulnerable package, its exploitability rating, and links to remediation resources.
Custom policy configurations allow teams to set their thresholds. For example, I’ve seen setups where only critical CVEs that affect production-bound artifacts trigger alerts, while others are logged passively. This approach cuts alert fatigue and makes security a visible but non-disruptive part of the developer experience.
Inspector also supports Lambda scanning, not just for dependencies, but also for actual function code. Standard scans review libraries, while code scans utilize machine learning to identify patterns such as hardcoded secrets, credential leaks, or risky API usage. Teams can now trigger scans via CLI and get actionable findings tied directly to AWS resources.
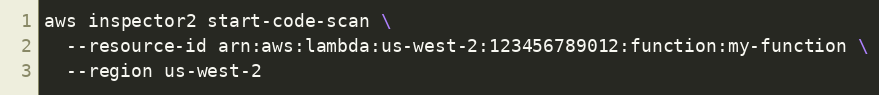
Figure 4: CLI command to initiate a Lambda function code scan using Amazon Inspector. Created by Naveen Sharma.
New generative AI features now recommend remediations, helping engineers act fast and stay aligned with secure coding best practices.
Reporting That Fits CI/CD Workflows
Photo: rawpixel.com | Freepik
Amazon Inspector integrates with Jenkins to bring security reporting directly into the CI/CD pipeline. Teams can generate SBOMs and scan results during builds and store them as part of the build artifacts.
The plugin supports:
- Automatic SBOM generation during builds
- Scan result storage in HTML, JSON, or CSV formats
- Threshold-based gating (e.g., fail builds with critical vulnerabilities)
- Audit-ready reports for review or long-term storage
This approach keeps security aligned with developer workflows, enabling earlier risk detection without extra dashboards or manual steps.
Implementation Guidance for DevSecOps Teams
Start with container builds in staging. It’s low-friction and creates muscle memory before expanding into serverless or production workloads. The most sustainable implementations I’ve seen start small and build confidence gradually, without overwhelming engineering or security teams. The key is to treat this as a progressive enhancement to your existing workflows.
Start Small and Expand
Most teams begin by integrating SBOM generation into container builds. This is the lowest-friction entry point and works exceptionally well for staging environments where experimental scans won’t block shipping.
From there, you can expand coverage to serverless components and apply Inspector’s Lambda-specific scanning features.
Ensure policies reflect your environment’s risk tolerance, such as allowing low CVEs but flagging any high-severity issues that affect public-facing assets.
Set Thresholds Gradually
Start by logging findings. Once the process is stable and developers trust the results, you can begin gating builds or deployments based on criticality thresholds. For example:
- Block deploys if 1+ critical CVEs exist
- Send Slack alerts if 5+ high CVEs appear
- Require owner sign-off for medium CVEs on regulated systems
These thresholds evolve as your tooling and confidence grow.
Don’t Forget Storage and Sharing
Don’t overlook centralized SBOM storage; it’s critical for audits and transparency. Whether you use S3, Artifact Registry, or a shared repo, keep these files versioned and accessible. This supports audit reviews, incident response, and cross-team transparency.
Real-World Results From Enterprise Rollouts
When integrated early, SBOMs and Inspector help teams catch vulnerabilities before code merges, not weeks later in production. In one enterprise rollout I advised, the use of Inspector reduced post-deploy vulnerabilities by over 60% within three months. The ticket resolution time dropped, and developers began to trust that security alerts were a signal, not noise.
In another case, an Inspector caught hardcoded credentials buried in a test Lambda function that had been overlooked for years. That single catch prevented what could have been a serious incident before it reached the production stage.
These kinds of improvements are possible when security becomes continuous, contextual, and collaborative.
Conclusion: Secure by Default, Not by Force
Security should never feel like a blocker. The combination of SBOMs and Amazon Inspector enables teams to integrate protection into the delivery pipeline without compromising speed or autonomy.
If you’re navigating pressure to deliver fast while maintaining trust, this is one workflow that deserves a place in your CI/CD process. It’s lightweight, extensible, and proven across modern architectures.