About 3 hours ago, everything went haywire. Bank terminals are getting BSODs, airlines are getting grounded, railway systems are malfunctioning, and everything seems to tie back to one company – Crowdstrike.

And that’s just the tip of the iceberg when it comes to the category of industries and sectors affected by a faulty OTA (supposedly) update from Crowdstrike which is one of the biggest cybersecurity providers in the world. Not only were Windows BSODs are surfacing everywhere but also recovery boot loops were also failing to do what they were supposed to do and instead joined the other side.
Client devices were not the only victims though because servers, whether on-premise or in the cloud were also getting bashed in the head as long as Crowdstrike’s solution was deployed.
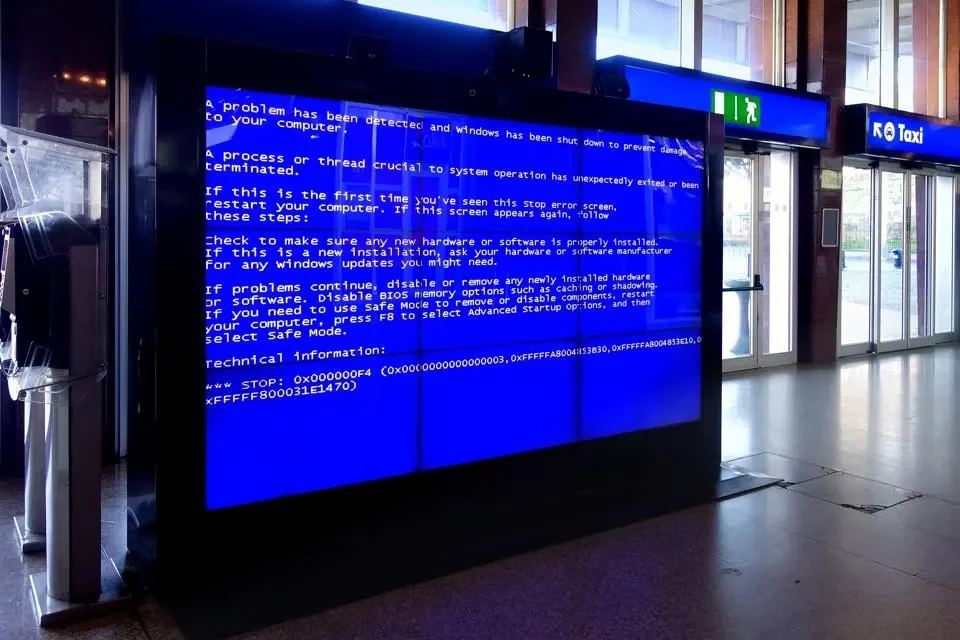
The first widespread report came from Australian banks, airlines, and TV broadcasters according to The Verge, then the EU region began to things started to hit the fan once the work hours started as airline company Ryanair reported a “third-party” IT issue affecting flight departures while Sky News based in the UK streamed an apology message for “broadcast interruption” so no morning news for the Brits unfortunately.
The rest of the world was also getting hit left and right – The US Federal Aviation Administration reports that all flights from Delta, United, and American Airlines are grounded due to a “communication issue while the Berlin airport is also warning of travel delays due to “technical issues” in addition to an airline in India has resorted to handwritten boarding passes due to the outages. Heck, even life-critical services like 911 emergency call centers in Alaska have also been impacted.
Due to the nature of the application and the OS it was designed for, even Microsoft themselves were allegedly part of the victim group due to service degradation notices related to Microsoft 365 services and apps. Official sources clarified that “configuration change in a portion of our Azure backend workloads.” was behind the minor shakeup but we won’t know for sure.
Despite the main culprit of the accident issuing a support note at 1:20 AM ET stating “We have widespread reports of BSODs on Windows hosts, occurring on multiple sensor versions,” and subsequently rolling back the faulty update, affected machines were still practically “bricked”, leaving businesses and organizations at shambles at the current moment.
The IT community did come around and put up a Reddit thread to get around the limitations by booting into the Windows Safe Mode environment, finding the Crowdstrike directory, and yanking a specific file. A cool workaround for client PCs and terminals but there will be challenges to get fixed in servers and cloud-based environments, and Crowdstrike better sort this out quickly.
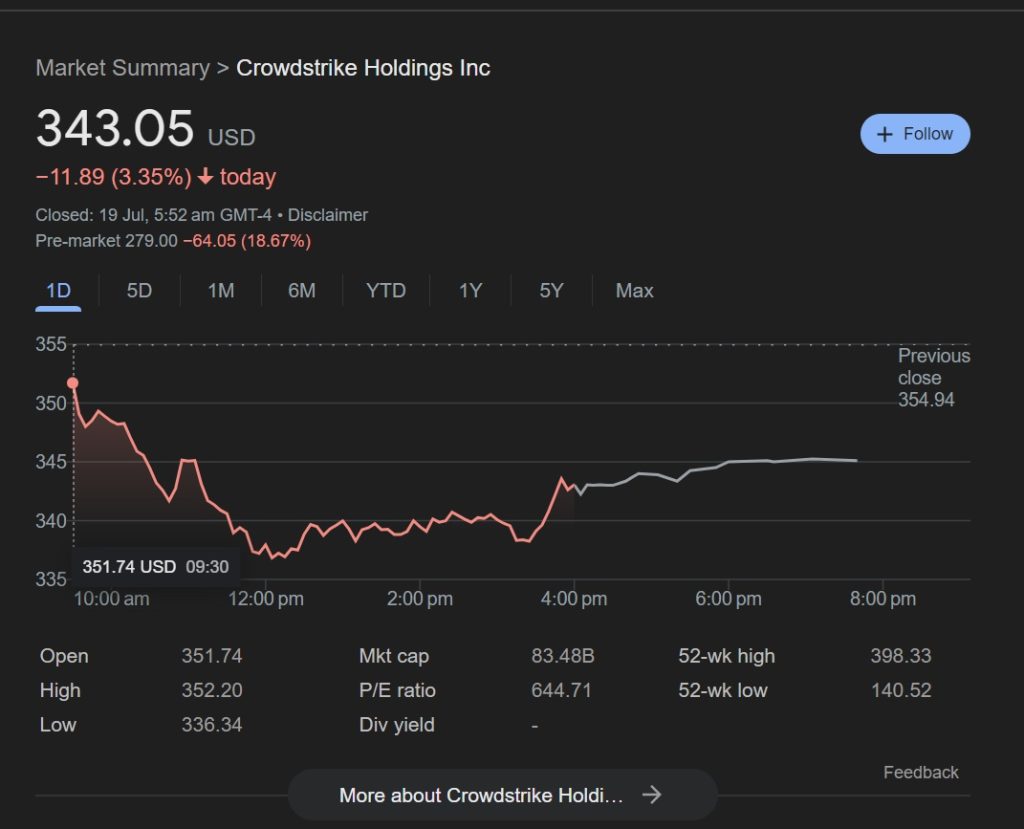
And just for funsies, that’s a dip yo.
Additional Sources: The Guardian, Channel News Asia, Forbes